Taqbit Labs

Quantum Cybersecurity Solutions
Founded 2022
Bangalore, India
$1+ million raised
15+ employees
Quantum CybersecurityPost-Quantum CryptographyQuantum Random Number GenerationSecure Communications

About Taqbit Labs

Taqbit Labs specializes in quantum cybersecurity solutions, including post-quantum cryptography and quantum random number generation (QRNG). The company helps organizations prepare for the quantum threat by implementing quantum-safe security measures to protect against attacks from future quantum computers.

Taqbit Labs is addressing the urgent need for quantum-safe cybersecurity. As quantum computers advance, they will be able to break current encryption methods, threatening the security of sensitive data. Taqbit Labs provides solutions including post-quantum cryptographic algorithms, quantum random number generators for truly unpredictable encryption keys, and consulting services to help organizations transition to quantum-safe security infrastructure.

Products & Solutions

Quantum Random Number Generator (QRNG)

Hardware-based true random number generation using quantum processes

  • •Certified randomness
  • •High-speed generation
  • •Compact form factor
  • •Easy integration

Post-Quantum Cryptography Suite

Software library implementing quantum-resistant encryption algorithms

  • •NIST-approved algorithms
  • •Drop-in replacement for existing crypto
  • •Performance optimized

Quantum Security Consulting

Assessment and migration services for quantum-safe security

  • •Risk assessment
  • •Migration planning
  • •Implementation support
  • •Training

Funding

Total Raised
$1+ million
Latest Round
Pre-Seed
Stage
Early Stage
Investors:Angel investors, Incubators

Latest News & Updates

View All Taqbit Labs News
EPB and IonQ Deploy Hybrid Trapped-Ion Algorithms on Forte Enterprise to Optimize Power Grid Topologyquantum-computing

EPB and IonQ Deploy Hybrid Trapped-Ion Algorithms on Forte Enterprise to Optimize Power Grid Topology

Municipal utility EPB, in collaboration with IonQ, has published experimental findings across three technical preprints demonstrating hybrid quantum-classical algorithms for distribution network reconfiguration (DNR). Funded under a $4 million grant from the National Institute of Standards and Technology (NIST), the project deployed EPB’s in-house Quantum Computing Fellows to execute optimization protocols on an on-premises IonQ Forte Enterprise trapped-ion system at the EPB Quantum Center in Chattanooga, Tennessee. The research benchmarks three distinct computational frameworks targeting active line-loss reduction and real-time switch allocation across distribution networks spanning up to 417 electrical buses. Constraint-Preserving Mathematical Encodings and Hardware Implementations DNR is a mixed-integer nonlinear programming challenge that requires selecting sectionalizing and tie switch states to minimize resistive dissipation while maintaining radial tree topologies without closed loops. Conventional quantum optimization approaches enforce radiality via penalty terms in Quadratic Unconstrained Binary Optimization (QUBO) matrices, introducing artificial energy barriers and barren plateaus. To bypass these issues, the joint research teams implemented three topology-preserving architectures directly on trapped-ion hardware: Technical Methodologies and Experimental Benchmarks across EPB-IonQ PreprintsComputational ArchitectureMathematical & Algorithmic EncodingDemonstrated Hardware & Simulation PerformanceQuantum-Enhanced Deep Reinforcement Learning (Q-DRL)Double Deep Q-Network (Double DQN) with a 4-layer Parameterized Quantum Circuit (PQC) backbone and double decision-head masking.Achieved 95.8% parameter reduction on the IEEE 33-bus system (9,156 parameters vs. 220,052 classically); IonQ Forte Enterprise execution yielded exact optimum (0.1396 MW loss) for 33 buses and within 0.30% of optimum for 69 buses.Subspace LR-QAOA with Guided MISOCP SolverCycle-ed

Quantum Computing ReportLoading...0
DataBrushing.AI Launches UEChain for Data Verification and Trustquantum-computing

DataBrushing.AI Launches UEChain for Data Verification and Trust

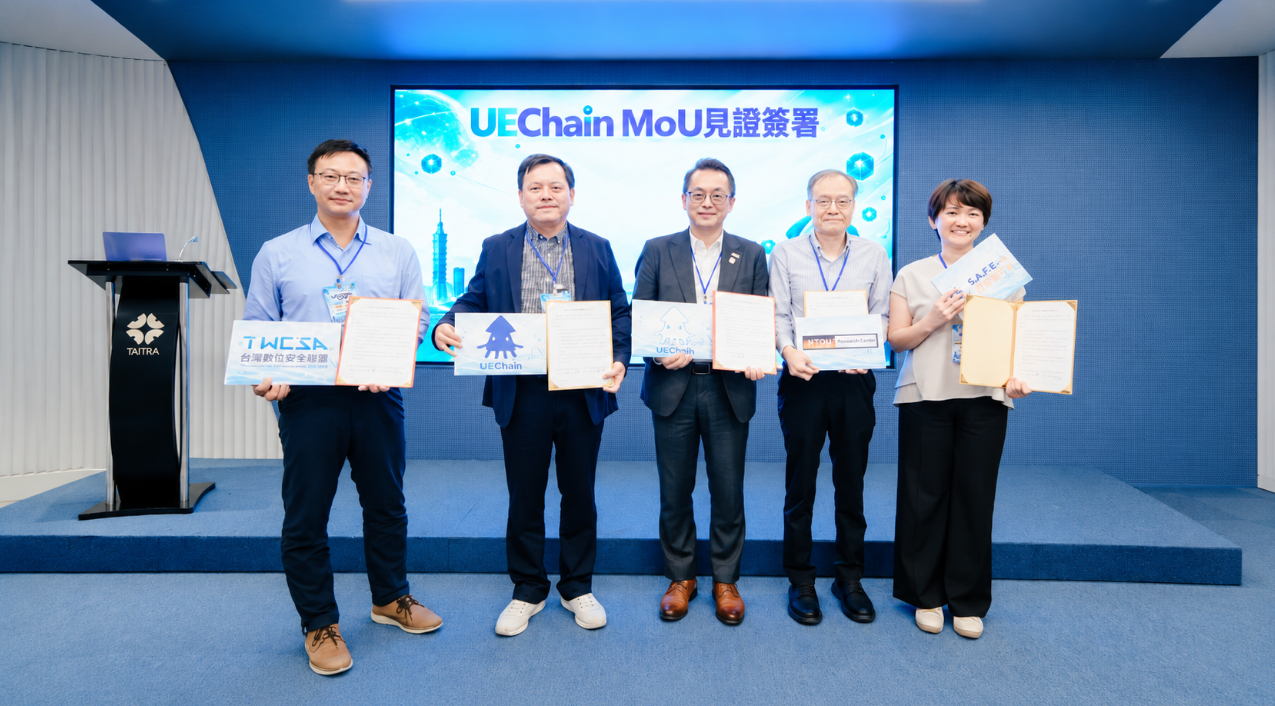
DataBrushing.AI Launches UEChain for Data Verification and Trust Mohib Ur Rehman October 28, 2026 Industry News Insider Brief DataBrushing.AI has launched UEChain, a trusted data platform that uses public key infrastructure (PKI), digital certificates, cryptographic signatures and timestamps to support data provenance and evidence verification. The platform supports conventional, hybrid and post-quantum cryptography, with APIs and SDKs for certificate verification and long-term evidence preservation. DataBrushing.AI has signed MOUs with four Taiwanese academic, research and cybersecurity organizations to explore applications including marine data protection, AI-era cyber defense and cross-institutional data security. PRESS RELEASE — AI DataBrushing Technology Co., Ltd. (DataBrushing.AI) launched S.A.F.E.-AI Trusted Platform – UEChain on October 16, a solution built on Public Key Infrastructure (PKI), a Certificate Authority (CA), and digital evidence chain technologies. UEChain is designed to help enterprises and research institutions answer three critical questions: Who provided the data? Has it been altered? And can its authenticity be independently verified? Guided by the principle “Turn Data into Evidence, Connect Evidence to Trust,” UEChain establishes an auditable trust mechanism across organization.s From Data Security to Verifiable Data Trust As generative AI, software supply chains, and cross-institutional data exchange become widespread, encryption alone cannot prove that a data source or version can be trusted. Without disclosing the original data, UEChain creates a cryptographic digest, digital signature, and timestamp for each record to preserve it as evidence, making that evidence fully traceable. PKI/CA and Secure Core: Building the Evidence Chain on Trusted IdentityUEChain uses X.509 digital certificates, public-key signatures, and certificate-chain validation to bind digital evidence to verifiable certificate identities, checking the chain of trust,

Quantum DailyLoading...0
AWS adds a new encryption method to guard data from future quantum attacksquantum-computing

AWS adds a new encryption method to guard data from future quantum attacks

The technology enables secure data exchange by establishing a 32-byte shared secret, designed to protect against future decryption by quantum computers. NIST designed ML-KEM to replace older schemes like DH/ECDH and RSA-based key transport as part of its strategic cryptographic roadmap. However, the service is not yet available in the Middle East (UAE), Middle East (Bahrain), and China Regions. ML-KEM Implementation Safeguards Against Future Quantum Attacks AWS KMS now uses Module-Lattice-Based Key-Encapsulation Mechanism (ML-KEM) adhering to the NIST FIPS 203 standard, a proactive measure against future decryption of currently recorded data. This implementation directly addresses the “harvest now, decrypt later” threat, where adversaries store encrypted data anticipating the arrival of sufficiently powerful quantum computers capable of breaking existing encryption. The KMS Encapsulate API generates a 32-byte shared secret and its ciphertext using the public key, while the Decapsulate API recovers the secret with the corresponding private key. AWS KMS safeguards the private key of each ML-KEM key pair within FIPS 140-3 Level 3 validated hardware security modules, providing a robust layer of protection. Customers can use the GetPublicKey API to export public keys for local encapsulation using libraries such as AWS-LC, OpenSSL, or Bouncy Castle, facilitating secure data exchange with external partners. According to the AWS announcement, NIST designed ML-KEM to replace classical key-establishment schemes, highlighting the importance of adopting post-quantum cryptography standards. The availability of ML-KEM-512, ML-KEM-768, and ML-KEM-1024 key specifications provides customers with options tailored to their specific security requirements. Source: https://aws.amazon.com/about-aws/whats-new/2026/10/kms-ml-kem-post-quantum/ More like thisQuantum CryptographyNIST lays out a plan for quantum-proof encryptionQuantum CryptographyKeyfactor maps five stages to quantum-safe cryp

Quantum ZeitgeistLoading...0
Quantum Beach 2026 — Official Livestreamquantum-computing

Quantum Beach 2026 — Official Livestream

Quantum Beach 2026 — Official Livestream Matt Swayne October 22, 2026 Industry News Join us online on October 22 as Quantum Beach 2026 brings researchers, entrepreneurs, investors and industry leaders to the Palm Beach County Convention Center in West Palm Beach, Florida. Explore the ideas, investments and partnerships shaping the quantum economy, from advances in quantum computing to the practical work of building businesses, preparing a skilled workforce and developing the infrastructure needed to support growth. With a focus on Florida and connections across the wider quantum community, Quantum Beach examines what it takes to move quantum technology from research toward commercial use. Watch the livestream below to follow the conversation and hear perspectives on the opportunities and challenges ahead. Keep track of everything going on in the Quantum Technology Market. In one place. Learn More Topics Quantum Beach, Quantum Beach 2026 Matt SwayneWith a several-decades long background in journalism and communications, Matt Swayne has worked as a science communicator for an R1 university for more than 12 years, specializing in translating high tech and deep tech for the general audience. He has served as a writer, editor and analyst at The Quantum Insider since its inception. In addition to his service as a science communicator, Matt also develops courses to improve the media and communications skills of scientists and has taught courses. [email protected] Share Stay Ahead of QuantumGet the latest research, company news, and market intelligence every week. Subscribe Free MENTIONED IN THE ARTICLE More in Industry News Qblox Integrates NVIDIA DGX Spark With Quantum System ControllerOctober 22, 2026ZuriQ and Rhonexum Partner on Cryogenic Electronics for Quantum ComputingOctober 22, 2026Ericsson Canada and ÉTS Partner on Quantum Computing ResearchOctober 22, 2026 Related Articles Industry NewsPalm Beach Colleges Connect as Florida Launches Quantum-Safe NetworkMatt

Quantum DailyLoading...0
Black Kite Adds Quantum Readiness Checks for Third-Party Vendorsquantum-computing

Black Kite Adds Quantum Readiness Checks for Third-Party Vendors

Black Kite Adds Quantum Readiness Checks for Third-Party Vendors Mohib Ur Rehman October 22, 2026 Industry News Insider Brief Black Kite has introduced Quantum Readiness controls within its Cyber Rating platform to assess observable signs of post-quantum cryptography readiness across an organization’s third-party vendors. The new controls examine indicators such as hybrid post-quantum key exchange, certificate signature readiness and assets without an identified migration path, integrating the results into the platform’s SSL/TLS Strength category. The feature is designed to help organizations track vendor readiness, identify potential gaps in supply-chain cryptographic security and prepare for post-quantum migration requirements. PRESS RELEASE — Black Kite, the leader in third-party cyber risk management, today announced the release of Quantum Readiness, a new set of controls within the SSL/TLS Strength category of the Black Kite Cyber Rating that evaluates quantum agility across an organization’s third-party vendor ecosystem. Quantum Readiness surfaces which vendors are quantum-ready or adopting quantum-safe encryption methods, providing an early indication of security maturity and preparedness for the post-quantum era. Quantum computers capable of breaking today’s encryption do not exist yet, but experts predict “Q-Day” could arrive as early as 2028. The risk is also retroactive: in “harvest now, decrypt later” attacks, bad actors are already collecting encrypted data to decrypt once quantum computers are powerful enough. Organizations need to prepare now – for many, the shift to quantum-safe encryption is underway, making quantum agility a key indicator of vendor security maturity and readiness. “Third-party cyber risk management needs to account for where risk is going, not only where it exists today,” said Ferhat Dikbiyik, Chief Research & Intelligence Officer (CRIO), Black Kite. “We built Quantum Readiness to give customers early visibility into quantum ag

Quantum InsiderLoading...0
South Korea picks telecoms operator KT to run two of three quantum test hubsquantum-computing

South Korea picks telecoms operator KT to run two of three quantum test hubs

Image: Original reporting by Cho Yun-Jin for Seoul Economic Daily · en.sedaily.com South Korea’s Ministry of Science and ICT will expand its quantum communication testing infrastructure with three new hubs, commercial, overseas and future, targeting completion by 2028. Building on testbeds established along the Seoul, Pangyo and Daejeon corridor since 2024, the project will see KT lead development of the commercial and future hubs, while SK Broadband focuses on overseas expansion. “To speed up the commercialization of quantum technology, it is important to broaden the testing infrastructure so that companies can verify their technology and products in a variety of environments,” according to an MSIT official. The three-year initiative will invest 7.4 billion won this year, combining government funding with private sector contributions. KT and SK Broadband Lead Expansion of Quantum Testbeds KT will extend the existing quantum test network to include Daegu this year, with planned expansions to Gwangju and Busan in the following year, and ultimately reaching the Gangwon region by 2028. This phased rollout aims to facilitate the application of quantum cryptography communications to critical data transmission in sectors like research, healthcare and finance, while simultaneously verifying the compatibility of equipment produced by various domestic manufacturers. The strategic expansion beyond the initial Seoul, Pangyo, and Daejeon corridor reflects a deliberate effort to broaden the accessibility and relevance of the testing infrastructure for a wider range of industries and potential users. SK Broadband is tasked with establishing the overseas hub, focusing on cross-border quantum security testing through connections with existing quantum testbeds in Singapore, Poland and Bulgaria. This international collaboration will employ quantum key distribution (QKD) for domestic and short-range overseas segments, while using cryptography (PQC) for long-haul international connecti

Quantum ZeitgeistLoading...0
Plurilock Files Information Circular and Schedules Shareholder Vote for C$33.8M ($24M USD) Acquisition by Quantum eMotionquantum-computing

Plurilock Files Information Circular and Schedules Shareholder Vote for C$33.8M ($24M USD) Acquisition by Quantum eMotion

Cybersecurity solutions provider Plurilock Security Inc. (TSXV: PLUR) has officially filed its management information circular and scheduled a special shareholder meeting for November 18, 2026, to vote on its proposed acquisition by quantum entropy and post-quantum cryptography developer Quantum eMotion Corp. (NYSE American: QNC; TSXV: QNC). First announced in late September 2026, the court-approved plan of arrangement values Plurilock at approximately C$33.8 million (~$24 million USD), representing total consideration of C$0.28 per share—a 100% premium over Plurilock’s 20-day volume-weighted average price prior to announcement. Under the agreed terms, Plurilock shareholders will receive C$0.084 in cash (30%) and 0.0763 of a Quantum eMotion common share (70%) for each share held. [ Quantum eMotion / Plurilock Transaction & Vote Timelines ]Transaction BenchmarkFinancial & Legal StructureKey Corporate & Regulatory Milestone• Transaction Valuation• Total Equity Value: C$33.8 million (~$24M USD)• C$0.28 per Plurilock share (100% premium over 20-day VWAP).• Consideration Split• 30% Cash (C$0.084) / 70% QeM Shares (0.0763)• Pro forma ownership: 95.97% existing QeM shareholders, 4.03% former Plurilock shareholders.• Shareholder Vote Date• Proxy Voting Deadline: Nov 16, 2026 (10:00 AM PST)• Special Meeting of Shareholders scheduled for November 18, 2026 in Vancouver, BC.• Target Closing & Delisting• Plan of Arrangement (Supreme Court of BC approval)• Expected closing late November 2026; Plurilock shares to be delisted from TSXV following completion. The transaction is designed to accelerate commercial adoption of Quantum eMotion’s quantum random number generators (QRNG) and FIPS 140-3/NIST 800-90B validated entropy technologies by embedding them into Plurilock’s established AI-driven identity, critical IT, and public-sector procurement channels across Canada, the U.S., and NATO alliance partners. Plurilock’s Board of Directors unanimously recommends that sha

Quantum Computing ReportLoading...0
Black Kite Introduces Quantum Readiness Controls to Assess Third-Party Cryptographic Riskquantum-computing

Black Kite Introduces Quantum Readiness Controls to Assess Third-Party Cryptographic Risk

Third-party cyber risk management platform provider Black Kite has announced the launch of Quantum Readiness, a new control set integrated into the SSL/TLS Strength category of its Black Kite Cyber Rating engine to evaluate post-quantum cryptographic (PQC) agility across third-party vendor supply chains. The feature provides organizations with external visibility into vendor cryptographic postures, identifying which third-party software, cloud, and IT providers have implemented quantum-resistant encryption methods—such as hybrid post-quantum key exchange and PQC certificate signature readiness—or remain reliant on legacy algorithms facing regulatory phase-outs. The rollout addresses mounting regulatory compliance deadlines, including U.S. Office of Management and Budget (OMB) M-26-15 guidelines mandating post-quantum key establishment by 2030 and digital signatures by 2031, Executive Order 14412 contractor migration targets, and European Union NIS2 supply chain cryptographic mandates. [ Black Kite Quantum Readiness Framework & Regulatory Benchmarks ]Assessment PillarExternal Observable SignalTarget Regulatory Compliance Driver• Key Exchange Agility• Detection of active hybrid PQC key exchange mechanisms• OMB M-26-15 U.S. Federal key establishment migration deadline (2030).• Certificate Readiness• Inspection of PQC-ready digital signature certificates• Executive Order 14412 Federal Acquisition Rule contractor standard (2030).• Asset Vulnerability Mapping• Identification of unmigrated legacy assets (RSA/ECDSA/ECDH)• NIST deprecation schedule (post-2030) and complete disallowance (2035).• Supply Chain Risk Integration• Integration into SSL/TLS Cyber Rating ecosystem scoring• EU NIS2 Directive supply chain risk management obligations (2026/2030). By automating continuous observation of external cryptographic signals across vendor supply chains, Black Kite aims to help enterprises and government agencies mitigate “harvest now, decrypt later” vulnerabilities prior to

Quantum Computing ReportLoading...0
Postquant Labs Launches Quip Virtual Machine to Unify Quantum Execution Across Hardware Architecturesquantum-computing

Postquant Labs Launches Quip Virtual Machine to Unify Quantum Execution Across Hardware Architectures

Quantum computing marketplace developer Postquant Labs has launched its Quip Virtual Machine (QVM) alongside its first quantum smart contracts on the Aglais testnet. Modeled conceptually after the Ethereum Virtual Machine (EVM), the QVM provides a constraint-based programming language and runtime designed to unify execution across annealers, gate-based quantum systems, and classical hardware. The platform introduces a gas-based cost model for quantum operations—calculating execution costs based on qubit space, run duration, and entanglement metrics—to quote maximum compute costs in shared credits prior to execution. Academic researchers from Monash University, the University of Notre Dame, and Purdue University are evaluating the runtime to streamline quantum algorithm development, while industrial optimization firm SiC Systems is testing the stack for AI-driven chemical and biological process modeling. [ Quip Virtual Machine (QVM) Technical & Operational Architecture ]Architecture PillarCore Technical MechanismTarget Operational Function• Cross-Hardware Language• High-level constraint-based programming abstraction• Compiles across annealers, gate-based QPUs, and classical solvers without manual circuit layout.• Gas-Based Cost Model• Dynamic pricing derived from qubit footprint, runtime, & entanglement• Quotes deterministic maximum compute costs upfront in network credits prior to job execution.• Live Portfolio Benchmark• 1,930 head-to-head races on Quip Network (D-Wave vs. CPU simulated annealing)• Quantum solver matched or beat classical across all trials; median win improved objective quality by 2.56%.• 3-Tier Verification• Classical simulation cross-checks & cryptographic attestations• Validates hardware execution accuracy and resolves output disputes against recorded benchmarks.• Settlement Layer• QuipSwap quantum-resistant payment framework• Handles decentralized program deployment, operator compensation, and transaction settlement. To evaluate per

Quantum Computing ReportLoading...0
Quantum Alliance forms amid warnings 6.4 million bitcoin face future quantum threat - CoinDeskquantum-computing

Quantum Alliance forms amid warnings 6.4 million bitcoin face future quantum threat - CoinDesk

TechQuantum Alliance forms amid warnings 6.4 million bitcoin face future quantum threatNine crypto companies launched the Quantum Alliance to jointly prepare for quantum attacks, but they disagree on when the threat will arrive and whether vulnerable BTC should be frozen.By Olivier Acuna|Edited by Jamie CrawleyOct 16, 2026, 6:52 a.m. EDT3 min read*]:whitespace-nowrap lg:hidden shrink-0">Make preferred on ShareShare this articleCopy linkX iconX (Twitter)LinkedInFacebookEmail*]:whitespace-nowrap hidden lg:inline-flex lg:ml-auto shrink-0">Make preferred on Experts have not been able to forecast a precise date when quantum computing will become an actual threat. (Planet Volumes/Unsplash)SummaryShowli::before]:size-[5px] [&_ol_li::before]:text-medium [&_ol_li::before]:leading-9 [&_ol_li::before]:content-[counter(ol-counter)] ">Experts warn that a future quantum computer could expose the secret keys of wallets holding an estimated 6.4 million bitcoin, including 1.1 million attributed to Satoshi Nakamoto, though no existing machine can do so.Researchers disagree on when the threat could emerge, with one citing 2028 as realistic, while a new industry alliance is developing standards to help blockchains adopt quantum-resistant security.Proposals to freeze, move or place vulnerable bitcoin in a trust have raised concerns about property rights and network neutrality, and any security upgrade would require broad coordination across the Bitcoin ecosystem.Who gets Satoshi Nakamoto’s 1.1 million bitcoin, and, for that matter, millions more that are at risk if quantum computers become powerful enough to break the security protecting it, has been a topic of intense debate for quite some time.Christopher Smith, CEO of quantum-resistant layer-1 blockchain Quantus, believes whoever develops that technology first could take those tokens worth billions, potentially with government backing.“The most likely scenario is that whoever gets the first CRQC (Cryptographically Relevan

Google News – Quantum ComputingLoading...0
Germany Issues Joint Federal PQC Migration Guidelines to Align with EU Post-Quantum Roadmapquantum-computing

Germany Issues Joint Federal PQC Migration Guidelines to Align with EU Post-Quantum Roadmap

The German Federal Ministry for Digital and State Modernization (BMDS), the Federal Ministry of the Interior (BMI), and the Federal Office for Information Security (BSI) have officially published their joint national guidelines (“Leitlinie zur Umstellung auf PQC“) detailing Germany’s strategy to migrate public and private digital infrastructure to Post-Quantum Cryptography (PQC). Following the formal release of the guidelines, the BSI issued an official press release highlighting that the national implementation framework directly operationalizes the European Union’s “Coordinated Implementation Roadmap for the Transition to Post-Quantum Cryptography,” adopted by NIS Workstream member states in June 2025. The publication emphasizes that rapid advancements in artificial intelligence (AI) are accelerating security research and attack methodologies against classical public-key encryption schemes (RSA, ECC), underscoring the necessity for crypto-agility—the ability to dynamically update cryptographic primitives and key lengths without disrupting underlying system architectures. [ Germany Federal PQC Migration Timeline & Risk Classifications ]Migration Phase & DeadlineTarget Risk Category & SystemsMandatory Technical Action Items• Phase 1: Readiness(Target: End of 2026)• All Federal, State, Municipal, and Critical Infrastructure (KRITIS) Entities• Establish cryptographic inventories (CBOMs) and Cryptographic Catalogs.• Formalize governance bodies and appoint responsible migration leads.• Adopt legally binding deadlines via IT-Planungsrat and UP KRITIS.• Phase 2: High-Risk Migration(Mandatory Deadline: 2030)• High-Risk Systems: Classified IT (VS-IT), long-term confidentiality data (“Store Now, Decrypt Later”), and critical infrastructure control.• Complete transition to BSI TR-02102 compliant post-quantum algorithms.• Enforce hybrid key exchange mechanisms (combining classical + PQC).• Deploy quantum-safe PKI and firmware/software update channels.• Phase 3: Ful

Quantum Computing ReportLoading...0